Built-in Multi-Factor Authentication

Secure accounts using OTP-based MFA without relying on third-party integrations.
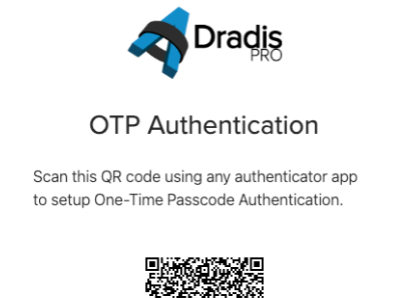
Screenshot of OTP

No third-party dependency

Dradis MFA runs entirely within your instance. There is no external authentication service, no SMS gateway, and no cloud provider in the loop.

For security teams handling sensitive assessment data, that means one fewer third party with access to your authentication flow. Supporting our data sovereignty and operational continuity guarantees.

Use any TOTP-compatible authenticator app: Google Authenticator, Authy, Microsoft Authenticator, or any other app that supports the standard.

Backup codes are generated at setup so users are never locked out.

Enforce MFA across the team

Admins can require MFA instance-wide from the admin console. This is useful for teams that need to demonstrate access controls for compliance frameworks such as SOC 2, ISO 27001, or PCI DSS, where strong authentication is an auditor expectation.

MFA is one part of a broader audit traceability posture in Dradis, alongside centralized permissions, audit logging, and structured review workflows.

Built for security teams, contributors, and clients

See plans

Seven Strategies To Differentiate Your Cybersecurity Consultancy

You don't need to reinvent the wheel to stand out from other cybersecurity consultancies. Often, it's about doing the simple things better, and clearly communicating what sets you apart.

  • Tell your story better
  • Improve your testimonials and case studies
  • Build strategic partnerships

Loading form...

Your email is kept private. We don't do the spam thing.